Banking & Financial Services
RBI and SEBI CSCRF alignment, transaction fraud monitoring and audited privileged access for core banking.
Cylentrix is the accountable enterprise technology partner for regulated organisations, unifying AI-driven cybersecurity, managed IT services and telecom solutions under one operating model. From 24/7 SOC and Zero Trust to cloud infrastructure, enterprise networking and compliance, we turn security into measurable business outcomes.
Cylentrix runs three deeply integrated practices: AI-driven cybersecurity, managed IT services and telecom solutions, under one accountable operating model. No vendor sprawl, no accountability gaps: one partner delivering managed security, cloud and enterprise networking with measurable outcomes.
Intelligence-led, Zero-Trust cyber operations for organisations where a breach is a headline. A 24/7 managed SOC, NGFW, EDR/XDR and continuous testing reduce dwell time and mean-time-to-respond, turning security from a cost centre into board-level assurance and audit-ready evidence.
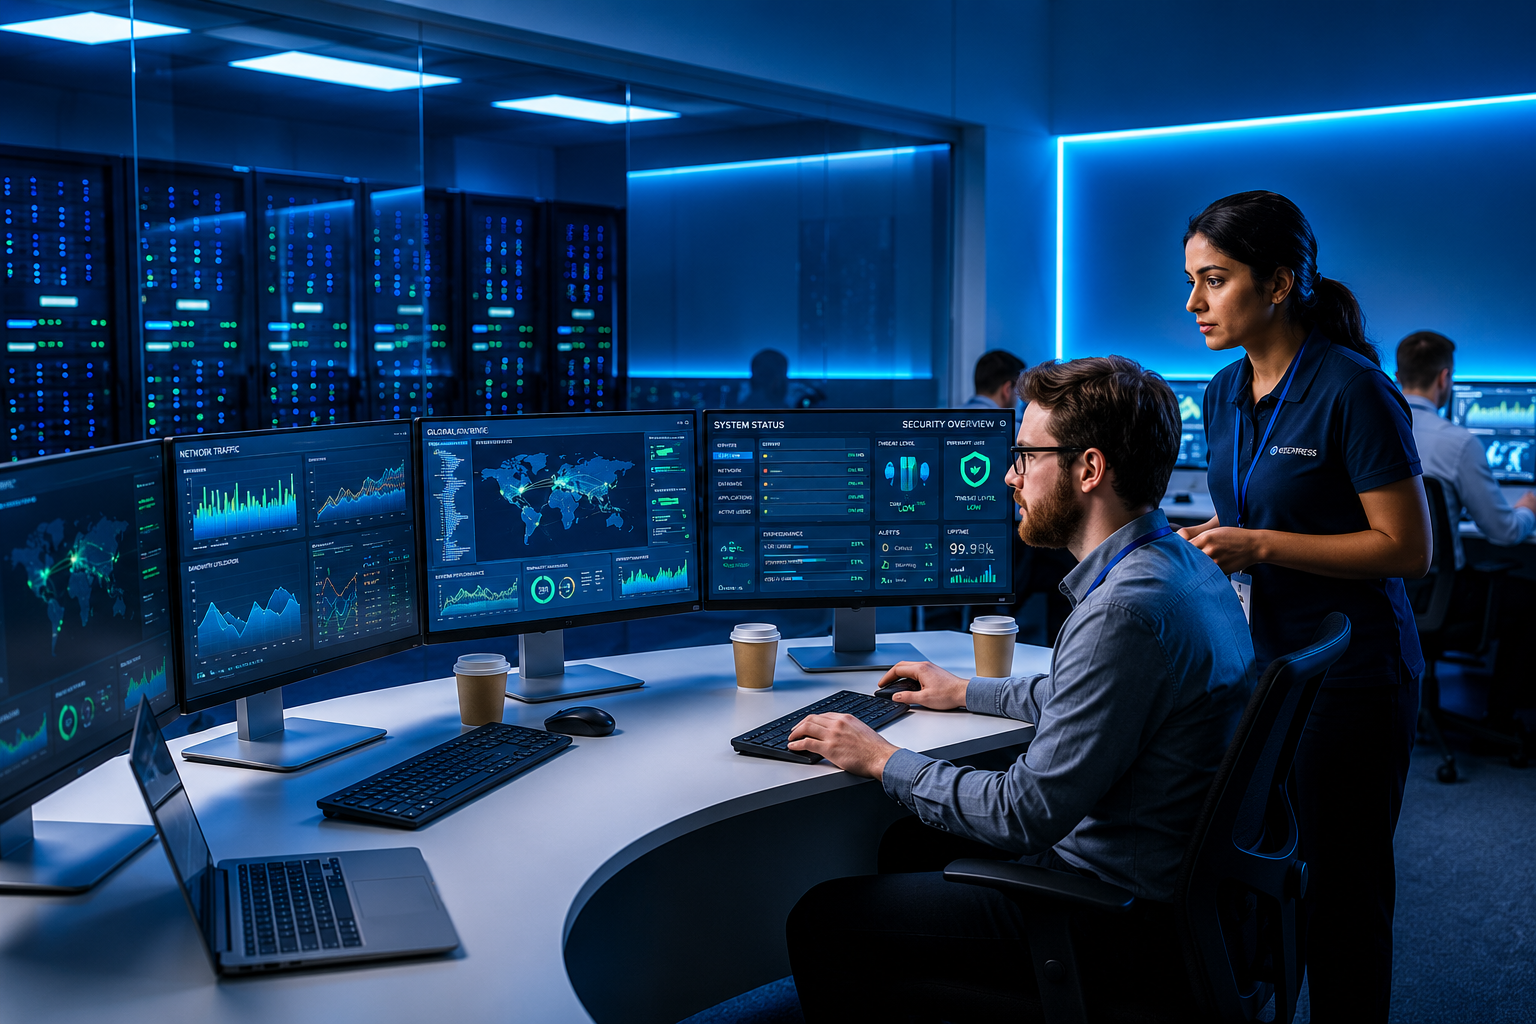
End-to-end managed IT spanning 24/7 NOC, cloud, data centre and helpdesk, run to enterprise SLAs. We consolidate vendors, cut cloud waste through FinOps, and keep high-availability infrastructure resilient, so IT becomes a lever for growth rather than an operational drag.
Always-on connectivity for organisations that cannot afford downtime. We engineer leased lines, private WAN, SD-WAN and enterprise voice into a single accountable stack, with managed CPE, carrier-neutral resilience and 24/7 NOC assurance that keeps every site, branch and data centre reliably online.
"Cylentrix doesn't deploy stacks. They rebuild operating models, and stay accountable for them, quarter after quarter."
Trusted across defence, finance, power, transport and public administration, delivering under the compliance and sovereignty demands of India's public sector.


From RBI-aligned BFSI to HIPAA-grade healthcare, Cylentrix engineers cybersecurity, managed IT and network infrastructure for regulated industries where compliance, uptime and audit readiness are not optional.

RBI and SEBI CSCRF alignment, transaction fraud monitoring and audited privileged access for core banking.
Patient data protection under HIPAA and DPDPA, plus segmentation for connected medical devices and HIS platforms.
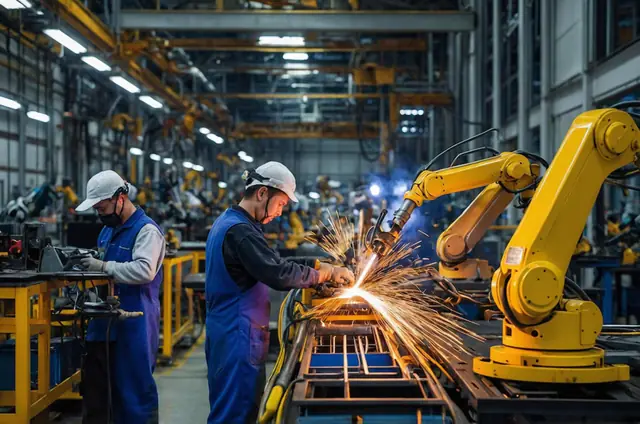
IT/OT boundary defence for SCADA and PLC environments, engineered around production uptime and safety.
Client-contractual security obligations, SOC 2 and ISO 27001 readiness, and secure multi-tenant delivery environments.
CERT-In compliant logging and reporting, empanelled audit support and data-localisation-aware architecture.
Campus network segmentation, student record protection and defence for high-volume BYOD populations.
PCI-DSS scope reduction, POS and payment-path hardening, plus bot and API protection for storefronts.
Warehouse and fleet system security, EDI and partner integration hardening, and third-party risk assurance.
Guest Wi-Fi isolation, PMS and booking-engine protection, and card-data security across distributed properties.
Tier III/IV colocation, carrier-neutral interconnect and hardened physical plus logical access control.
Every Cylentrix engagement follows the same disciplined operating cadence, from discovery to optimisation, with named accountability, Zero Trust design and audit evidence at each gate of your digital transformation.
Asset, risk and connectivity baseline. Stakeholder workshops, threat-model and current-state architecture review.
Target-state blueprint mapped to regulatory frameworks. Deliverable: HLD, LLD, RACI, runbook scaffolding.
Phased build with controlled cutovers, change management, and integrated testing, measured against acceptance criteria.
24/7 managed operations: SOC, NOC, incident response, vulnerability management, under enterprise SLAs.
Quarterly business reviews, FinOps tuning, threat-posture maturity uplift, continuous control improvement.
Outcomes delivered across regulated industries: measured, audited, and signed-off by client steering committees. No marketing math.
Consolidated 4 disparate SIEMs into a unified SOC operating model, mapped to MITRE ATT&CK, with hardened IR runbooks across 1,400+ endpoints.
Replaced legacy MPLS with hybrid SD-WAN over ILL + LTE underlay; saved 38% on annual connectivity spend with carrier-grade resilience.
HIPAA-aligned cloud landing zone, automated FinOps controls and Tier-III DR, completed within a 9-month phased plan with zero data-loss events.
Zero-Trust segmentation, NGFW deployment and OT-aware monitoring across 11 plants, with no production downtime during cutover.
Verbatim feedback from Cylentrix client steering committees across BFSI, healthcare and retail. We earn enterprise references the slow way, through delivered outcomes.
Cylentrix transformed our connectivity and security posture. The SOC took ownership in week one, and downtime fell off a cliff.
From cloud migration to managed IT, they delivered exactly what was scoped: on time, on cost, audited at every gate.
Their P2MP and SD-WAN engineering simplified 600-store operations dramatically. The technical depth is real.
Pragmatic, vendor-agnostic research on AI security, Zero Trust and enterprise networking, written by the engineers who run the operations, not analysts pitching from a deck.
Aligned to global frameworks and regulator expectations, and engineered with the evidence trail to prove it during any third-party audit.
Cylentrix's controls, SOC playbooks and engagement artefacts are mapped to the major global and Indian regulatory frameworks. Each engagement ships with a control-evidence pack mapped to the relevant standards.




Share a few details and a Cylentrix security or networking specialist will come back to you with a scoped response, not a sales pitch. Under NDA on request.
Curated from CIO, CISO and infrastructure leadership briefings. For deeper detail, request a confidential briefing pack.
Talk to a solutions architectA Cylentrix managed cybersecurity engagement spans 24/7 SOC monitoring, SIEM/SOAR operations, NGFW management, EDR/XDR, vulnerability management, threat hunting, IR retainer and a quarterly maturity uplift programme, under enterprise SLAs and named client-success leadership.
We model commercials as outcome-linked managed services with a baseline run-rate plus consumption components for cloud, connectivity and incident workloads. Multi-pillar engagements (cyber + IT + telecom) typically deliver 18-30% lower TCO vs siloed vendors over 24 months.
For Managed SOC, time-to-value is typically 21-45 days from contract, with controlled cutovers, parallel run, and signed-off acceptance gates. Connectivity and data-centre projects are scoped against site-survey outputs and carrier provisioning windows.
Engagements default to in-country hosting (India / Singapore / US) with documented data flows, encryption at rest/in transit, and contractual residency commitments. We map controls to RBI, SEBI, IRDAI, DPDPA and GDPR depending on the client's regulatory footprint.
Yes. Our offensive-security practice runs as an independent unit: black-box, grey-box and assumed-breach assessments, plus continuous attack-surface management. Findings are walked through with engineering and remediated under tracked SLAs.
A Cylentrix ILL is symmetrical, dedicated bandwidth at 1:1 contention, with carrier-grade SLAs (99.5%+ uptime), static IPs, and 24/7 NOC visibility. We bundle it with managed CPE, optional SD-WAN, and NGFW for a single accountable connectivity stack.
Book a 30-minute consultation with a Cylentrix security and networking specialist, under NDA on request. No slideware, no upsell.